Platform
One Integrated RegTech Ecosystem
Identity, screening, risk, review, monitoring and intelligence operate on a shared record. Products can be deployed modularly and integrated with the institution's existing systems — so a decision made at onboarding remains visible, explainable and auditable years later.
Architecture concept
How the ecosystem fits together
A conceptual view of the compliance flow. Each layer is configurable to the institution's risk appetite and regulatory environment.
- 01
Digital Identity
Individuals and businesses are verified once and carried through the rest of the workflow on a single record.
- 02
Financial Crime Screening
Sanctions, PEP and adverse media screening applied inside the same case as the identity data.
- 03
Risk Assessment
Configurable risk assessment applied consistently across customers, products and markets.
- 04
Compliance Review
Named officer review, escalation and approval — with four-eyes controls where the institution requires them.
- 05
Monitoring & Intelligence
Ongoing re-screening and regulatory intelligence feeding back into the record.
- 06
Audit & Reporting
A retained, exportable record of what was decided, by whom, when and on what basis.
Product modules around the flow
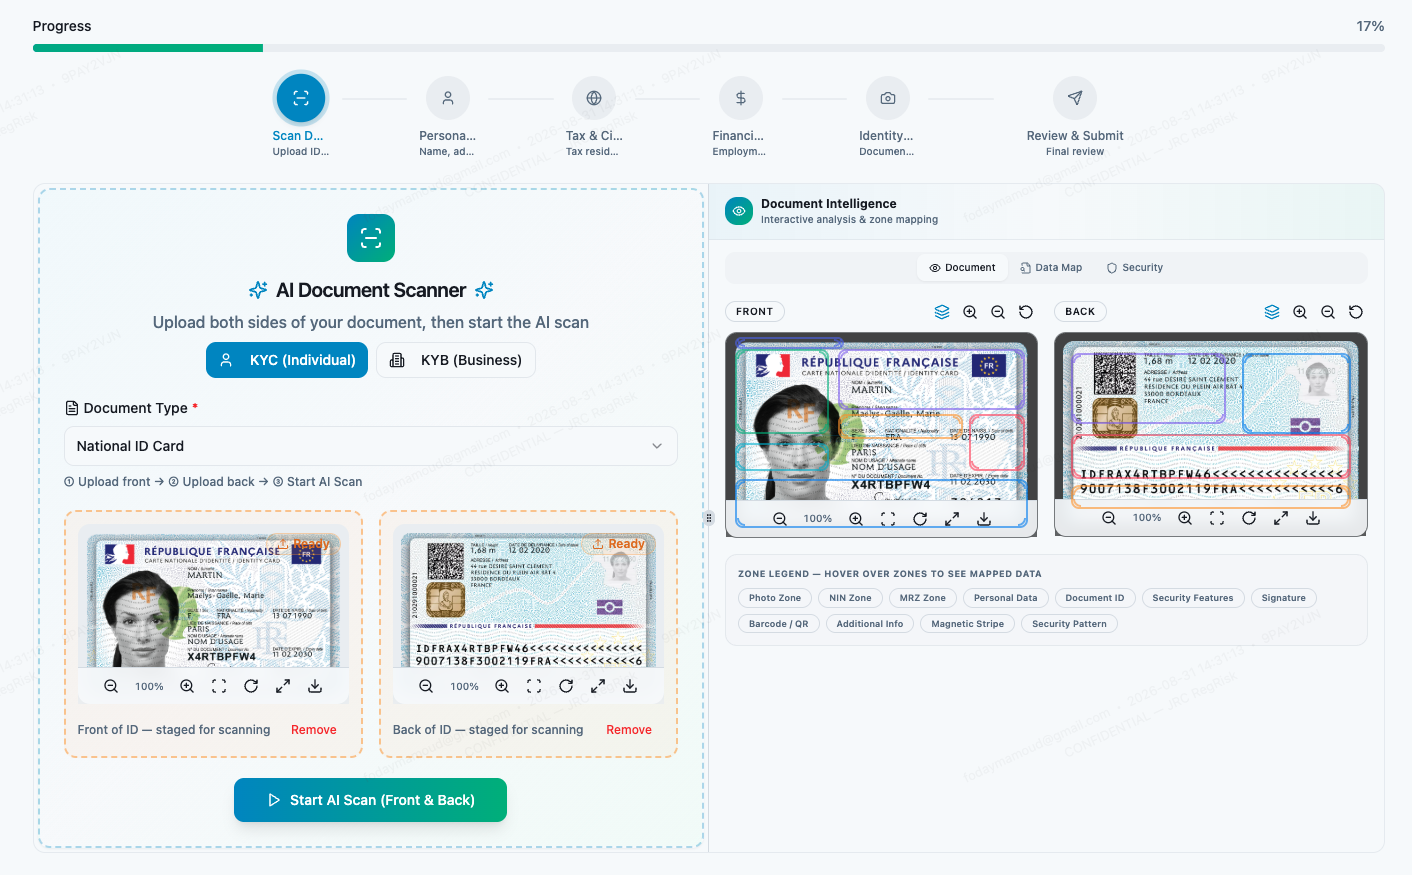
Digital Identity Verification, KYC/KYB & Financial Crime Risk
IdentityProof
Verify individuals and businesses, screen them for financial crime risk and record a defensible decision in one integrated platform.
Learn moreSanctions, PEP & Adverse Media Screening
PEP & Sanctions Screening
Screen customers and counterparties against PEP and sanctions data, with structured match review, risk assessment and auditable screening outcomes.
Learn moreDigital AML/CFT & Compliance Training
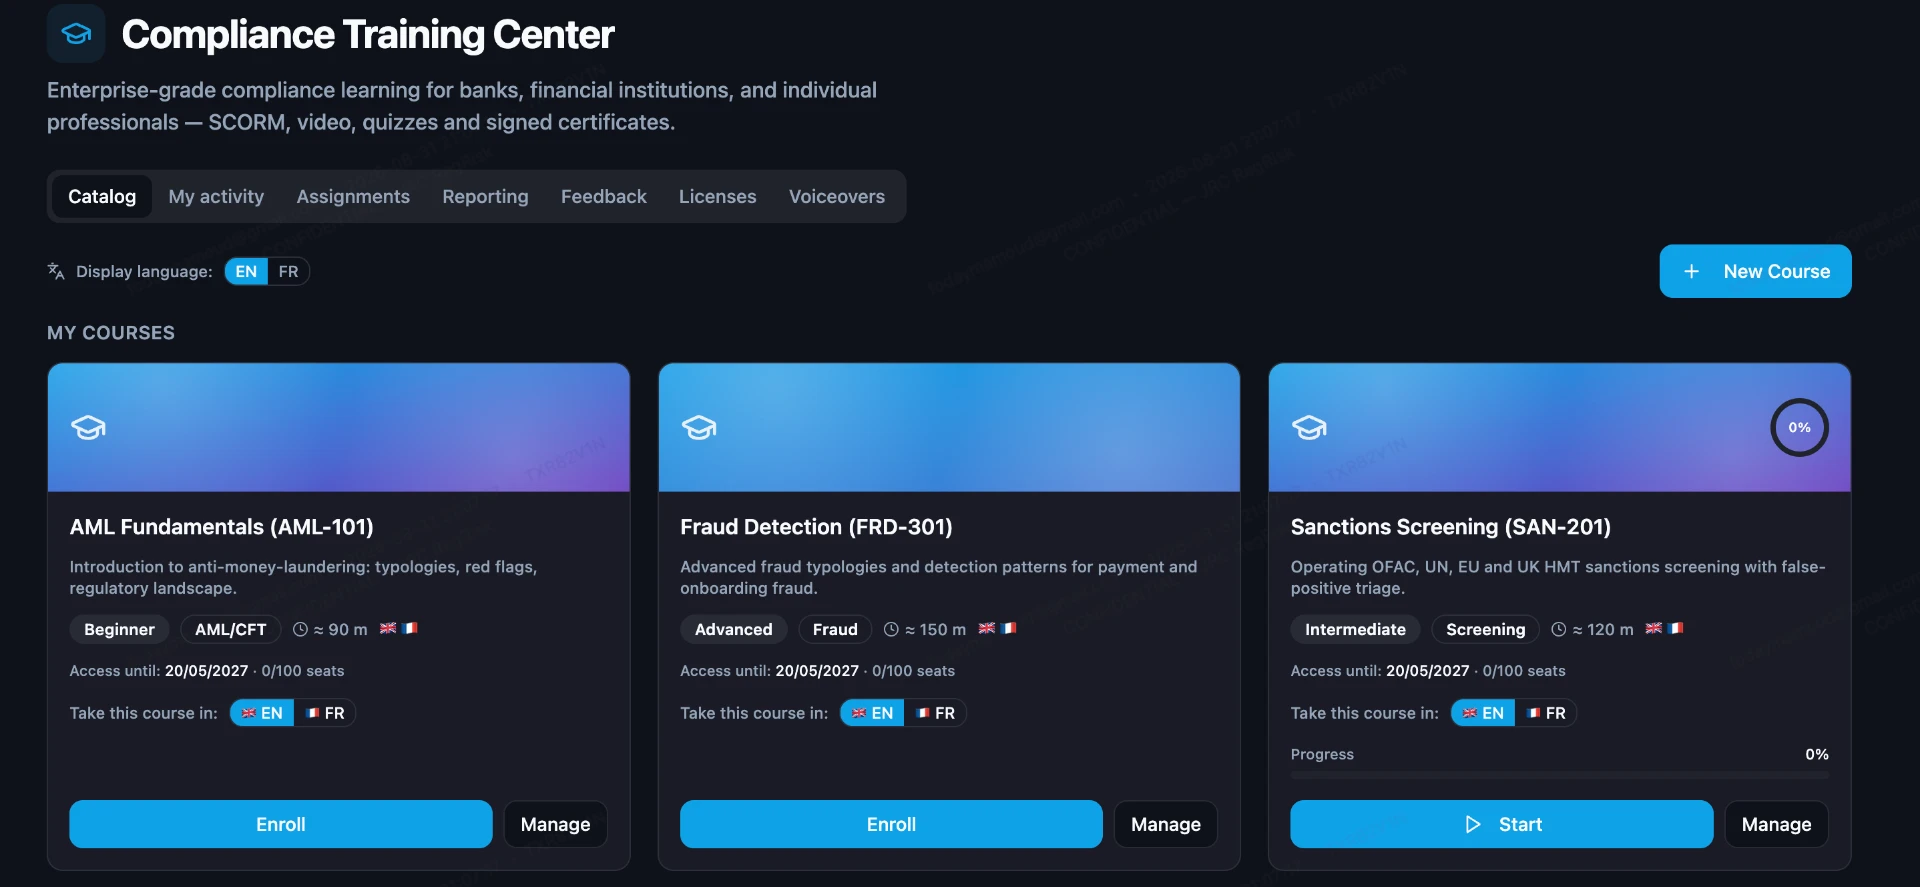
Compliance Training Centre
An institution-wide digital AML/CFT and compliance training platform for regulated financial institutions and compliance teams.
Learn moreRegulatory Intelligence & Compliance Monitoring
RegRisk Intelligence
Follow regulatory developments and translate them into practical compliance actions your institution can evidence.
Learn moreAML/CFT, KYC/KYB, Sanctions, Fraud, Governance & Regulatory Advisory
Advisory & Professional Services
Regulatory and financial crime advisory delivered alongside technology, from framework design to implementation support.
Learn moreMarket Research & Surveys
Market Intelligence
Structured market research and intelligence gathering across African and European financial sectors, delivered through JRC RegRisk's dedicated survey platform.
Open the platformWorkflow
Platform in action
The standard end-to-end path from first capture to a retained audit record.
- 01Identity
- 02Verify
- 03Screen
- 04Assess Risk
- 05Review
- 06Monitor
- 07Audit
Identity
Capture individual or business identity data
Verify
Validate documents and identity attributes
Screen
Sanctions, PEP and adverse media
Assess Risk
Apply configurable risk rules
Review
Compliance officer decision
Monitor
Ongoing re-screening and review
Audit
Retained, exportable case record
Deployment
Modular by design, integrated by default
Institutions adopt what they need. Modules share identity, risk and audit services rather than duplicating them.
Layer 1
Interface layer
Compliance workspace, case queues, dashboards and reporting for officers and supervisors.
Layer 2
Service layer
Verification, screening, risk assessment, monitoring and training services shared across modules.
Layer 3
Record layer
Case data, decisions, reviewer identity and audit history retained for evidencing.
Security & trust
Built to withstand institutional scrutiny
Platform controls and design characteristics that support review by internal audit, external auditors and supervisors.
Data Protection
Controls over storage, transmission and retention of case data.
Role-Based Access
Permissions aligned to compliance roles and segregation of duties.
Auditability
Every action retained with reviewer, timestamp and rationale.
Human Review
Decisions recorded against named compliance officers.
Secure API Integration
Authenticated integration with core institutional systems.
Enterprise Architecture
Environment and deployment design for regulated institutions.
Demo & sandbox access
Controlled access to the JRC RegRisk environment
Sandbox access is provided through a controlled evaluation process.
- STEP 1
Request Access
- STEP 2
JRC RegRisk Approval
- STEP 3
Secure Sandbox Access
Approved organisations receive named, time-limited access to a controlled evaluation environment.